Your Master of Ceremonies
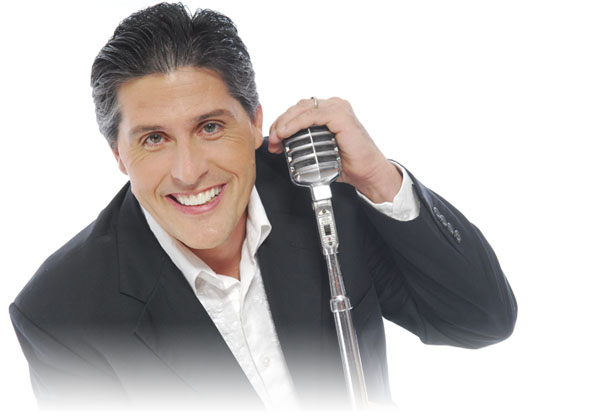
Erick Olson
Corporate Magician & Comedian
Think Jay Leno meets David Copperfield. Erick Olson keeps CyberDefenseCon moving with sleight of hand, sharp one-liners, visual gags and plenty of audience participation, so expect to be pulled into the act.
Between sessions he performs strolling close-up magic, and his quick wit has made him a favorite with McDonald’s, Walt Disney World, Nabisco, IBM and Verizon.
Day One Keynotes

The Myth of Mythos
Ira Winkler, CISSP
CEO, CruiseCon · Former Field CISO, Walmart
Ira Winkler, CISSP is CEO of CruiseCon and President of Secure Mentem. He is considered one of the world’s most influential security professionals, and has been named a “Modern Day James Bond” by the media. Ira is one of the foremost experts in the human elements of cyber security and is known for the extensive espionage and social engineering simulations that he has conducted for Fortune 500 companies globally. He continues to perform these espionage simulations, as well as assisting organizations in developing cost effective security programs. Ira is a noted speaker, media contributor and author of several books most notably Spies Among Us, Corporate Espionage and Zen and the Art of Information Security. He and his work have been featured in a variety of media outlets including CNN, The Wall St Journal, USA Today, San Francisco Chronicle, Forbes, among other outlets throughout the world.
Winkler began his career at the National Security Agency, where he served as an Intelligence and Computer Systems Analyst. After leaving government service, he went on to serve as President of the Internet Security Advisors Group, Chief Security Strategist at HP Consulting, and Director of Technology of the National Computer Security Association. He has also served on the graduate and undergraduate faculties of the Johns Hopkins University and the University of Maryland.
Strategies for Implementing Microsegmentation within existing Production Environments
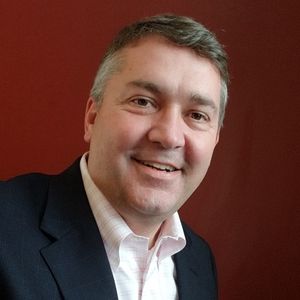
Michael Hoehl
CISO, Carpenter Technology
Michael Hoehl, CISO at Carpenter Technology, is a business-driven cybersecurity executive with more than 20 years of experience leading global security programs that strengthen enterprise resilience and support business growth. His expertise spans security operations and incident response, governance and audit, identity and access management, risk management, and regulatory compliance. Michael brings broad experience from across manufacturing (OT), financial services, healthcare, government, and retail environments, with industry recognition from Forbes, the ORBIE, and Cyber Defense Magazine.
Michael’s credentials include a Master of Science in Information Security Management from SANS Technology Institute and several certifications including Carnegie Mellon University CISO and CDAIO program, CISSP, GCIH, and GCIA. His published papers include: “Framework for building a Comprehensive Enterprise Security Patch Management Program”; “Proposal for standard Cloud Computing Security SLAs – Key Metrics for Safeguarding Confidential Data in the Cloud”; and, “Creating a monthly Information Security Scorecard for CIO and CFO”. He is also a graduate of the FBI CISO Academy.
Abstract
The purpose and benefits of Microsegmentation are well known. It is foundational to Zero Trust and essential for Compliance (e.g., PCI DSS, CMMC 2.0, etc.). However, implementing Microsegmentation to protect critical systems (e.g., Payment Card Systems, Hospital Clinical Systems, HR Systems, SCADA/Manufacturing Systems, etc.) remains a challenge for most organizations. This session shares approaches and lessons learned that leaders can use to save time, save money, reduce risk, and increase credibility implementing Microsegmentation successfully.
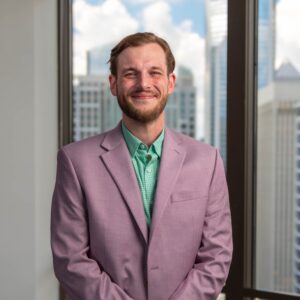
Chris Rose
Managing Director, AEGIS at Arcova
Chris Rose leads data security and AI enablement at the enterprise level. An early mover in responsible AI adoption, he built an AI-enablement service specialization ahead of the market and has delivered modern data protection and DSPM programs across multi-cloud estates for global enterprises, along with a Fortune 500 cryptography center of excellence focused on post-quantum readiness. His work centers on a practical question: how organizations adopt the technologies redefining their risk, AI first among them, without losing control of their data.
Chris is Managing Director of AEGIS at Arcova, a security architecture, engineering, and infrastructure practice he built from the ground up, now backed by more than 35 specialists serving Fortune 500 and critical infrastructure clients. He advises CISOs, CIOs, and boards on turning technical exposure across AI, cloud, IT, and OT into defensible investment decisions, and holds IEC 62443 Level 4 and NERC CIP credentials along with Idaho National Laboratory’s Cyber-Informed Engineering training.
Clint Bodungen
OT Cybersecurity Pioneer & AI Engineer · Director of AI/ML Engineering, Arcova
Clint Bodungen is an OT cybersecurity pioneer and AI engineer with 30+ years of experience. Known for pioneering practical, innovative approaches to cybersecurity, he has spent the last two decades at the forefront of integrating gamification and AI into cybersecurity and training. He has published two books, Hacking Exposed: Industrial Control Systems and ChatGPT for Cybersecurity Cookbook, and created ThreatGEN® Red vs. Blue, an online cybersecurity simulation game, as well as AutoTableTop, an AI-driven incident response platform that uses AI to build and run IR tabletop exercises. Today, as Director of AI/ML Engineering at Arcova, his work centers on creating and deploying production-ready AI systems that help transform and modernize the cybersecurity industry.
Day Two Keynotes
The Silent Killers in Your Supply Chain: Surviving the Third-Party Risk Apocalypse
Mark Dunkerley
CISO, Coca-Cola Bottlers’ Sales & Services
Mark is the author of Resilient Cybersecurity: Reconstruct your defense strategy in an evolving cyber world. Building a Comprehensive Cybersecurity Program addresses the current challenges and knowledge gaps in cybersecurity, empowering individuals and organizations to navigate the digital landscape securely and effectively. Readers will gain insights into the current state of the cybersecurity landscape, understanding the evolving threats and the challenges posed by skill shortages in the field. This book emphasizes the importance of prioritizing well-being within the cybersecurity profession, addressing a concern often overlooked in the industry.
Read more
You will construct a cybersecurity program that encompasses architecture, identity and access management, security operations, vulnerability management, vendor risk management, and cybersecurity awareness. It dives deep into managing Operational Technology (OT) and the Internet of Things (IoT), equipping readers with the knowledge and strategies to secure these critical areas. You will also explore the critical components of governance, risk, and compliance (GRC) within cybersecurity programs, focusing on the oversight and management of these functions. This book provides practical insights, strategies, and knowledge to help organizations build and enhance their cybersecurity programs, ultimately safeguarding against evolving threats in today’s digital landscape.
The Future of AI Security
Vivek Kumar
Global Chief Information Security Officer, Alter Domus
Vivek Kumar is the Global Chief Information Security Officer at Alter Domus, bringing more than 25 years of IT and cybersecurity experience, primarily within the financial sector.
He leads global information security, risk management, and cybersecurity operations, with a focus on building resilient security programs, high-performing teams, and effective governance. His experience includes large-scale security operations, technology consolidation, executive and board-level reporting, and advising security companies on product strategy and emerging challenges.
Kumar is also an active industry speaker and was named a 2026 Top Global CISO by Cyber Defense Magazine in recognition of his leadership, innovation, and contributions to cybersecurity.
Continuous Control Assurance & X-ROC: From Static Assessments to Living Risk Intelligence
Lalit Ahluwalia
CEO & Founder, DigitalXForce
Lalit Ahluwalia is the CEO and Founder of DigitalXForce and iTrustXForce, where he leads innovation in real-time GRC automation and Cybersecurity Mesh Architecture. He also created XForce Galaxy’s cyber escape rooms, which teach cybersecurity through play, and the “Security-in-the-Box” framework.
Earlier in his career, he was CEO and Global Cybersecurity Head of Inspira Enterprise, Global Head of Client Security Solutions and Risk Services at Wipro, and Managing Director and North America Security Lead for Health and Public Sector at Accenture, and he worked on security initiatives at Deloitte and PwC.
He is Chairman of the US India Chamber of Commerce and a former member of the Forbes Technology Council. His honors include the Dallas Business Journal’s 40 Under 40, D CEO’s Excellence in Cybersecurity award, the Tech Titans Emerging Company CEO Award (2025) and a place on D CEO’s Dallas 500 (2026).
Abstract
Annual assessments, periodic control testing and static risk registers were built for an enterprise that no longer exists. Cloud configurations drift, identities sprawl and AI agents multiply between audits — and that widening “assurance gap” is where undetected risk grows. Lalit Ahluwalia makes the case for Continuous Control Assurance (CCA) and the X-ROC (Risk Operations Center): an operating model that fuses security, GRC, identity, cloud and third-party telemetry into living risk intelligence. He walks through a six-stage loop from raw data to measurable risk reduction, shows how it plays out in financial services, healthcare and critical infrastructure, and closes with a five-step playbook — identify, connect, automate, correlate, measure — so CISOs can stop reporting compliance and start proving to the Board that risk is actually going down.
Dr. Garfield Jones
SVP Global Strategy & Research, QuSecure
Dr. Garfield Jones is currently the Senior Vice President, Research & Technology Strategy at QuSecure. He is a renowned technical advisor and test and systems engineering manager with extensive knowledge of IT and DoD systems.
Prior to joining QuSecure, Dr. Jones served as Associate Chief of Strategic Technology for the Cybersecurity and Infrastructure Security Agency (CISA). In this role, he developed the strategy and guidance on using innovative, leading-edge technology across CISA, including articulating and documenting the future technology vision to achieve mission objectives and goals. Dr. Jones led the post-quantum cryptography initiative at CISA, consulting with executive branch level staff on crafting and disseminating guidance for federal agencies and national policy on research development and adoption of PQC technology.
Specifically, Dr. Jones worked with the Office of Management and Budget (OMB), Office of National Cyber Director (ONCD), and various federal agencies to execute tasks outlined in executive orders 14306 (Sustaining Select Efforts to Strengthen the Nation’s Cybersecurity) and 14144 (Strengthening and Promoting Innovation in the Nation’s Cybersecurity) and memos such as OMB 23-02 (Migrating to Post-Quantum Cryptography) issued by the Executive Branch.
Expert Panelists
Teri Green
Vice President of Technology, Elevate
Teri Green is an international speaker, award-winning technology executive, author, and advocate for equity in tech. Born and raised on the South Side of Chicago, she brings resilience, authenticity, and purpose to every stage she stands on and every organization she leads.
Read more
With nearly two decades of leadership experience spanning roles from director to chief information officer and chief information security officer, Green serves as vice president of technology at Elevate, where she oversees cybersecurity, data and analytics, DevOps, infrastructure and systems, data strategy, and information technology for a national nonprofit. She holds a Master’s degree in Cybersecurity Information Assurance from Penn State University and is currently pursuing a PhD in Policy and Law with a minor in cybersecurity at Purdue University.
Matt Morton
Assistant Vice President & CISO, University of Chicago
Matt Morton is the Assistant Vice President and CISO at the University of Chicago and leads the Security Engineering, Operations, IAM and Information Administration parts of the Office of the CISO. Previously CISO for the University of Nebraska System, he also consulted at Vantage Technology.
Read more
With 18 years in security leadership, he holds multiple certifications. He speaks on AI security and governance, is completing a doctorate, and enjoys fly fishing, hiking and attending his children’s events.
Anthony Siravo, MBA, MSIS
Chief Information Security Officer, Brown University Health
Anthony Siravo is Chief Information Security Officer at Brown University Health, where he leads enterprise cybersecurity strategy, risk governance, and incident response across eight hospitals and more than 250 outpatient locations. His focus includes ransomware resilience, medical device and IoT/IoMT security, cloud security, regulatory alignment, and executive-level cyber risk communication.
Read more
He previously served as CISO at Zebra Technologies, leading global enterprise and product security across more than 240 international locations. With more than two decades of CIO and CISO leadership experience, Anthony aligns cybersecurity with business, patient-care, and regulatory priorities, including HIPAA, HITRUST, PCI DSS, NIST, and ISO 27001. He holds an MBA and MS in Information Systems from Bryant University, a BA from Roger Williams University, and multiple cybersecurity certifications. His honors include CSO50 awards, CyberDefenseCon Top Global CISO recognition from 2023–2025, and OnCon Icon Top 100 Information Security Professional recognition.
Andy Neller
Chief Information Security Officer, GreatAmerica Financial Services
Andy Neller is Chief Information Security Officer at GreatAmerica Financial Services, where he leads cybersecurity strategy, governance, and risk oversight. With almost 30 years of experience, Andy focuses on aligning cybersecurity with business priorities, building strong teams, and translating complex risks into clear executive and board decisions.
Read more
He holds CISSP, C|CISO, and CRISC certifications and chairs the Technology Association of Iowa’s CISO Workgroup.
Sam Masiello
Chief Information Security & Privacy Officer, The Anschutz Corporation
Sam Masiello is the Chief Information Security and Privacy Officer at The Anschutz Corporation. Sam has been working with email, messaging, and fighting internet pollution for over 25 years.
Read more
Prior to The Anschutz Corporation, he served as the CISO at Gates Corporation, where he was responsible for the company’s data security, risk, and global compliance initiatives. Before that, he was CISO at TeleTech, where he oversaw the protection of employee, consumer, and customer data for all of the organization’s clients, which included many Fortune 500 companies.
Michael Prakhye
CISO & Director of Information Security, Adventist HealthCare
Michael Prakhye serves as a Chief Information Security Officer and Director of Information Security at Adventist HealthCare. With 20 years of experience in the healthcare industry and the DoD, Michael has a deep understanding of the unique challenges faced by healthcare organizations when it comes to data security.
Read more
He holds a Master’s in Cyber Security and a Master’s in Business Administration from the University of Maryland, as well as Executive Healthcare Leadership and Change Management certificates from Cornell University. Michael also holds industry certifications including Project Management Professional, C|CISO, ITIL, CISSP, and others.
As a healthcare executive and Chief Information Security Officer, Michael is dedicated to ensuring that patient data is secure and confidential. In addition to his expertise in information security, he is also well-versed in healthcare compliance, risk management, and privacy. Michael understands the importance of balancing security needs with operational efficiency and is committed to finding solutions that achieve both.
Dan Carbonnell
Vice President & CISO, InteLogix
Dan Carbonnell is Vice President and Chief Information Security Officer at InteLogix, where he leads the company’s enterprise security program and LogixGuard, its managed security services practice. With more than 29 years of experience, including over 25 years with Fortune 500 companies, Dan also chairs InteLogix’s Digital and AI Advisory Council and serves on its CEO-led AI Task Force.
Read more
A recognized cybersecurity leader and industry speaker, Dan has been named a Top Global CISO by Cyber Defense Magazine for four consecutive years (2023–2026) and a Top 10 Information Security Professional in the 2026 OnCon Icon Awards. He is also an active community leader with extensive nonprofit, volunteer firefighting, and civic service experience.
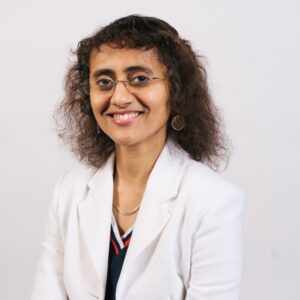
Priya is an accomplished Cybersecurity and Risk Management Executive with ~20 years of demonstrated experience also covering Privacy, Compliance, and Digital Resiliency. She is currently the CISO at University of Alberta. Before moving to Canada, she spent close to a decade advising global Financial Services, including some of the largest names in Wall Street & Technology organizations in New York & the Bay Area.
Read more
She has a commendable history of both collaborating with Senior Leadership and the Boards of large global companies to formulate robust and agile cyber / risk strategies, and working with the operational teams to implement them, and building trusted relationships with stakeholders internally and externally.
As a recognized leader in the space, she is invited to chair and speak at global summits / conferences including ISACA, ISC2, BlackHat among others, and has received quite a few global CISO & DEI awards. She also authors global thought leadership publications. Priya’s global exposure working in the US, UK, Canada, China, India for multinational organizations equips her with a global mindset and the ability to work and communicate effectively with people from different backgrounds and disciplines, being empathetic & adaptable.
Day 1
Tuesday, October 20, 2026
-
8:00 – 9:00 am
MealConference Breakfast
Sponsored by Cyber Defense Ventures
-
9:00 – 9:30 am
AI KeynoteThe Myth of Mythos
Ira Winkler, CruiseCon · Sponsored by UnknownCyber
-
9:40 – 10:10 am
Zero Trust KeynoteStrategies for Implementing Microsegmentation within existing Production Environments
Michael Hoehl, CISO, Carpenter Technology
-
10:15 – 10:25 am
BreakCoffee & Networking Break
-
10:30 – 11:00 am
Live PitchesLive “Whale Tank” Innovator Pitches to All CISOs
Live voting
-
11:05 – 11:20 am
Guest SpeakerManisha Arora
Co-founder & CEO, WoolyAI
-
11:25 – 11:55 am
KeynoteSponsored Keynote by Arcova
-
12:00 – 1:00 pm
MealLunch
Sponsored by Cyber Defense Ventures
-
1:00 – 2:30 pm
ShowcaseInfoSec Innovators Showcase
-
2:45 – 3:55 pm
RoundtablesCISO Roundtables / Coffee Break + Showcase
-
4:00 – 4:45 pm
-
4:50 – 5:05 pm
TalkKurt Olson
Chief Strategy Officer, Cyber Defense Ventures
-
5:10 – 5:30 pm
Guest SpeakerAmir Ofek
AIZome
Day 2
Wednesday, October 21, 2026
-
8:00 – 9:00 am
MealConference Breakfast
Sponsored by Cyber Defense Ventures
-
9:00 – 9:30 am
OT KeynoteThe Silent Killers in Your Supply Chain: Surviving the Third-Party Risk Apocalypse
Mark Dunkerley, CISO, Coca-Cola Bottlers’ Sales & Services
-
9:40 – 10:10 am
AI KeynoteThe Future of AI Security
Vivek Kumar, Global CISO, Alter Domus
-
10:15 – 10:45 am
GRC KeynoteContinuous Control Assurance & X-ROC: From Static Assessments to Living Risk Intelligence
Lalit Ahluwalia, CEO & Global Cybersecurity Head, DigitalXForce
-
10:45 – 11:10 am
BreakCoffee & Networking Break
-
11:15 – 11:45 am
Live PitchesLive “Whale Tank” Innovator Pitches to All CISOs
Presenting: DigitalXForce, Ridge Security Technology, Sevii, ThreatLocker, Unknown Cyber Inc. · Live voting
-
12:00 – 1:00 pm
MealLunch
-
1:00 – 2:30 pm
ShowcaseInfoSec Innovators Showcase
-
2:30 – 3:30 pm
RoundtablesCISO Roundtables / Coffee Break + Showcase
-
3:40 – 3:55 pm
Quantum ExpertGuest Speaker: Dr. Garfield Jones
SVP Global Strategy & Research, QuSecure
-
4:00 – 4:45 pm
Schedule subject to change at any time.
CISO Roundtables
20 topics across 5 tracks
Small-group sessions hosted by award-winning infosec innovator experts during the afternoon roundtable blocks on both days.
AI, Automation & Future Tech
- Autonomous SOCs & AI-Driven Threat ResponseHow CISOs are preparing for fully automated detection, triage, and containment.
- AI Safety, Model Security & Emerging RegulationsPreparing for global AI governance frameworks, “AI Bills of Materials,” and model-risk audits.
- Securing AI Supply Chains: Training Data, Models & Inferencing RisksThe new attack surface: poisoning, model theft, LLM jailbreaks, and malicious model updates.
- Quantum Readiness & Post-Quantum Cryptography RoadmapsWhat boards expect by 2030 and how to actually make a migration plan.
- Synthetic Identity & AI-Augmented Fraud PreventionHow criminals are weaponizing generative identities and voice cloning.
Cloud, Infrastructure & Architecture
- Multi-Cloud Resilience: Failure Modes, Backups & InteroperabilityAvoiding a catastrophic cloud provider outage or regional cloud collapse.
- Container, Kubernetes & Microservices Security at ScaleEmerging attack patterns in ephemeral and serverless environments.
- Edge Computing, 5G, and Distributed Enterprise SecurityManaging risk when compute moves out of the data center and closer to the user.
- Secure Digital Transformation & Technical Debt EradicationHow CISOs reduce inherited risks while modernizing legacy infrastructure.
- Identity Fabric & Unified Access Control for Distributed WorkforcesMoving beyond IAM silos toward a single enterprise identity strategy.
Threat Landscape & Defensive Evolution
- Deepfakes, Voice Cloning & Social Engineering 3.0Protecting executive teams, PR, and brand reputation in an era of perfect AI mimicry.
- Advanced Persistent Manipulation (APM): The New Hybrid Attack PatternAttacks that combine cyber, misinformation, extortion, and psychological operations.
- AI-Accelerated Malware & Autonomous Offensive ThreatsPreparing for malware that learns, adapts, and updates itself faster than human defenders.
- Cross-Border Cyber Warfare & Global Cyber SanctionsHow geopolitics and national security pressures affect enterprise risk.
Governance, Leadership & Organizational Maturity
- CISO Liability, Insurance Shifts & Personal Risk MitigationNavigating increasing laws that hold CISOs personally accountable.
- Security Budget Optimization in an AI-Economized FutureWhere budgets shift as AI replaces human-heavy processes.
- Cybersecurity Workforce 2030: Upskilling, Automation & Talent StrategyHow AI, automation and new roles reshape staffing strategies.
- Board-Level Cyber Resilience: Communicating Risk in the Age of AIWhat directors expect from CISOs in 2026 and beyond.
Risk, Resilience & Enterprise Protection
- Fourth-Party & Nth-Party Risk: Mapping the Hidden Supply ChainMoving past vendor management into the ecosystem you don’t control.
- Digital Resilience & Crisis Simulations for AI-Enhanced IncidentsPreparing for fast-moving crises with playbooks that adapt in real time.
Topics subject to change at any time.
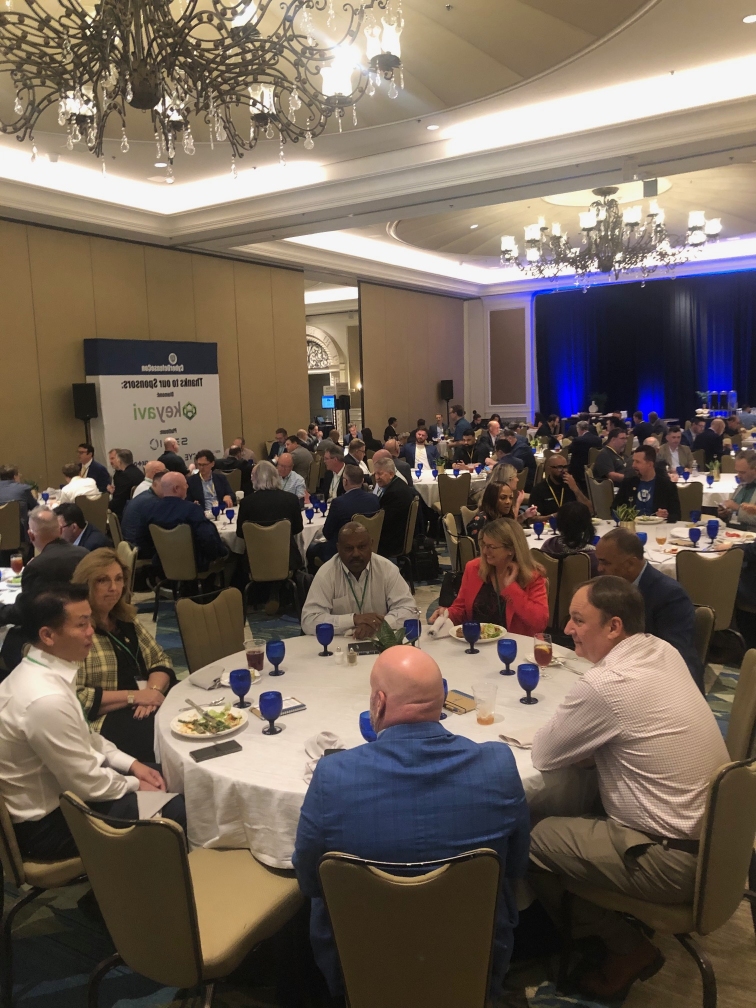

Call for CISO Speakers, Panelists & Roundtable Leaders
CyberDefenseCon 2026 invites speaker proposals to present to our Top Global CISO audience at The Ritz-Carlton, Orlando, Florida. Speakers should be willing to lead CISO roundtable sessions during the conference, as well as participate in CISO panel discussions, if requested.